Vesper logs in like a real attacker, maps your whole web app and API, and refutes its own findings before it reports them. Evidence, not noise, from a terminal or a governed console, with or without AI. Built for teams of every size and industry, from startups to the largest enterprises.
Traditional scanners fire thousands of findings, most of them false, and only test the anonymous surface. They miss the broken object level authorization, privilege escalation and business logic flaws that cause real breaches. Vesper inverts that: it authenticates, explores everything before and after login, and refutes its own findings so your team spends time on real issues, not triage.
Burp scan · Acunetix · Nessus
Verified · authenticated · fast
Consultancy · PTaaS
Vesper sits between the two: the depth and proof of a manual authenticated pentest, at a price and speed you can run every release.
Every authorization finding runs an adversarial refute: reproduce as the attacker, confirm the owner can reach it so the object is real, and require it to fail unauthenticated. Public by design results and flukes are quarantined, not reported. Injection, XSS, CRLF, SSRF, forged tokens and unauthenticated reachability re-run their own experiment the same way, 22 of 36 modules in all, and the per finding verification record ships in the scan metadata.
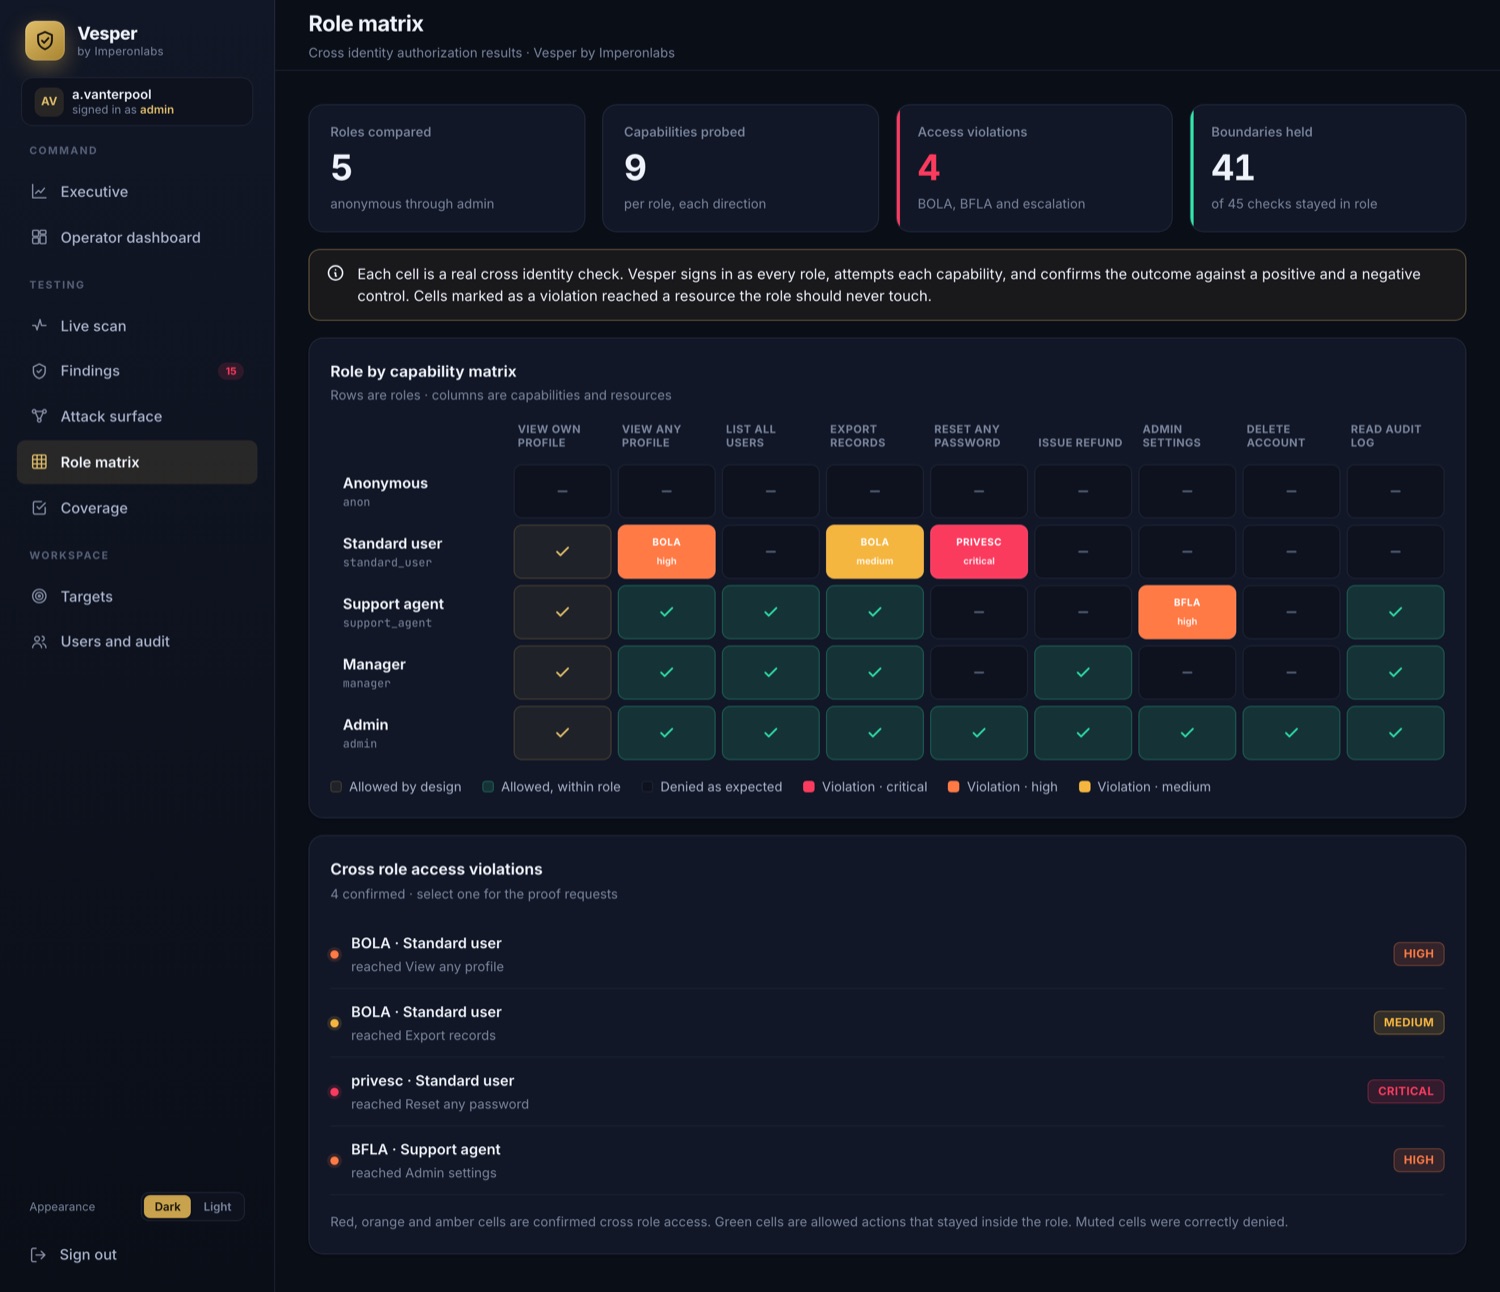
Password login, cookie or session, paste a JWT or cookies, or configure an MFA / TOTP seed. Add multiple roles and Vesper builds a full cross identity BOLA, BFLA and privilege escalation matrix.
All detection is deterministic and runs with no AI at all. Optionally plug in your own model key for AI triage and attack planning. Your data, your key, your choice.
Every scan emits mapped SAMA CSF, ISO 27001 and SOC 2 control reports in HTML, CSV and JSON alongside the pentest report. They are auditor ready and GCC first.
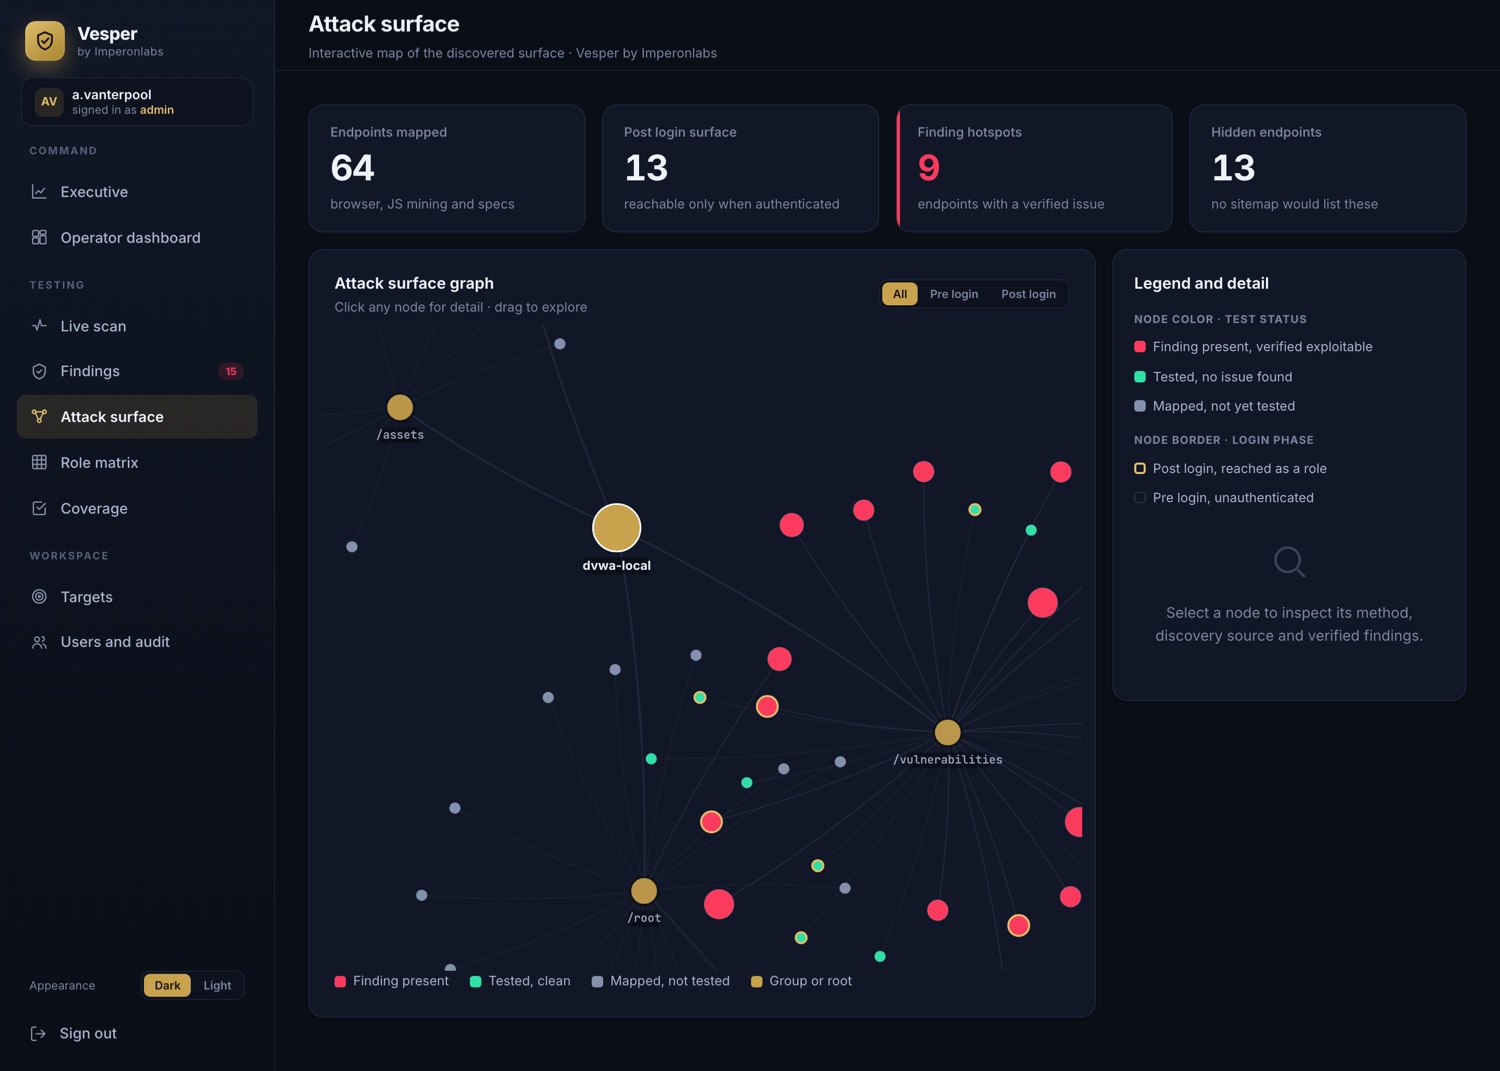
Headless browser and HTTP crawling, every JS file mined for hidden endpoints, before and after login. It also ingests OpenAPI, Postman and HAR natively, and records a session so you can replay a logged in flow.
Drop the CLI into CI and agent pipelines with exit code gating and SARIF, or run governed scans from the web console with role based access control, scan history, rescan and Slack and email alerts.
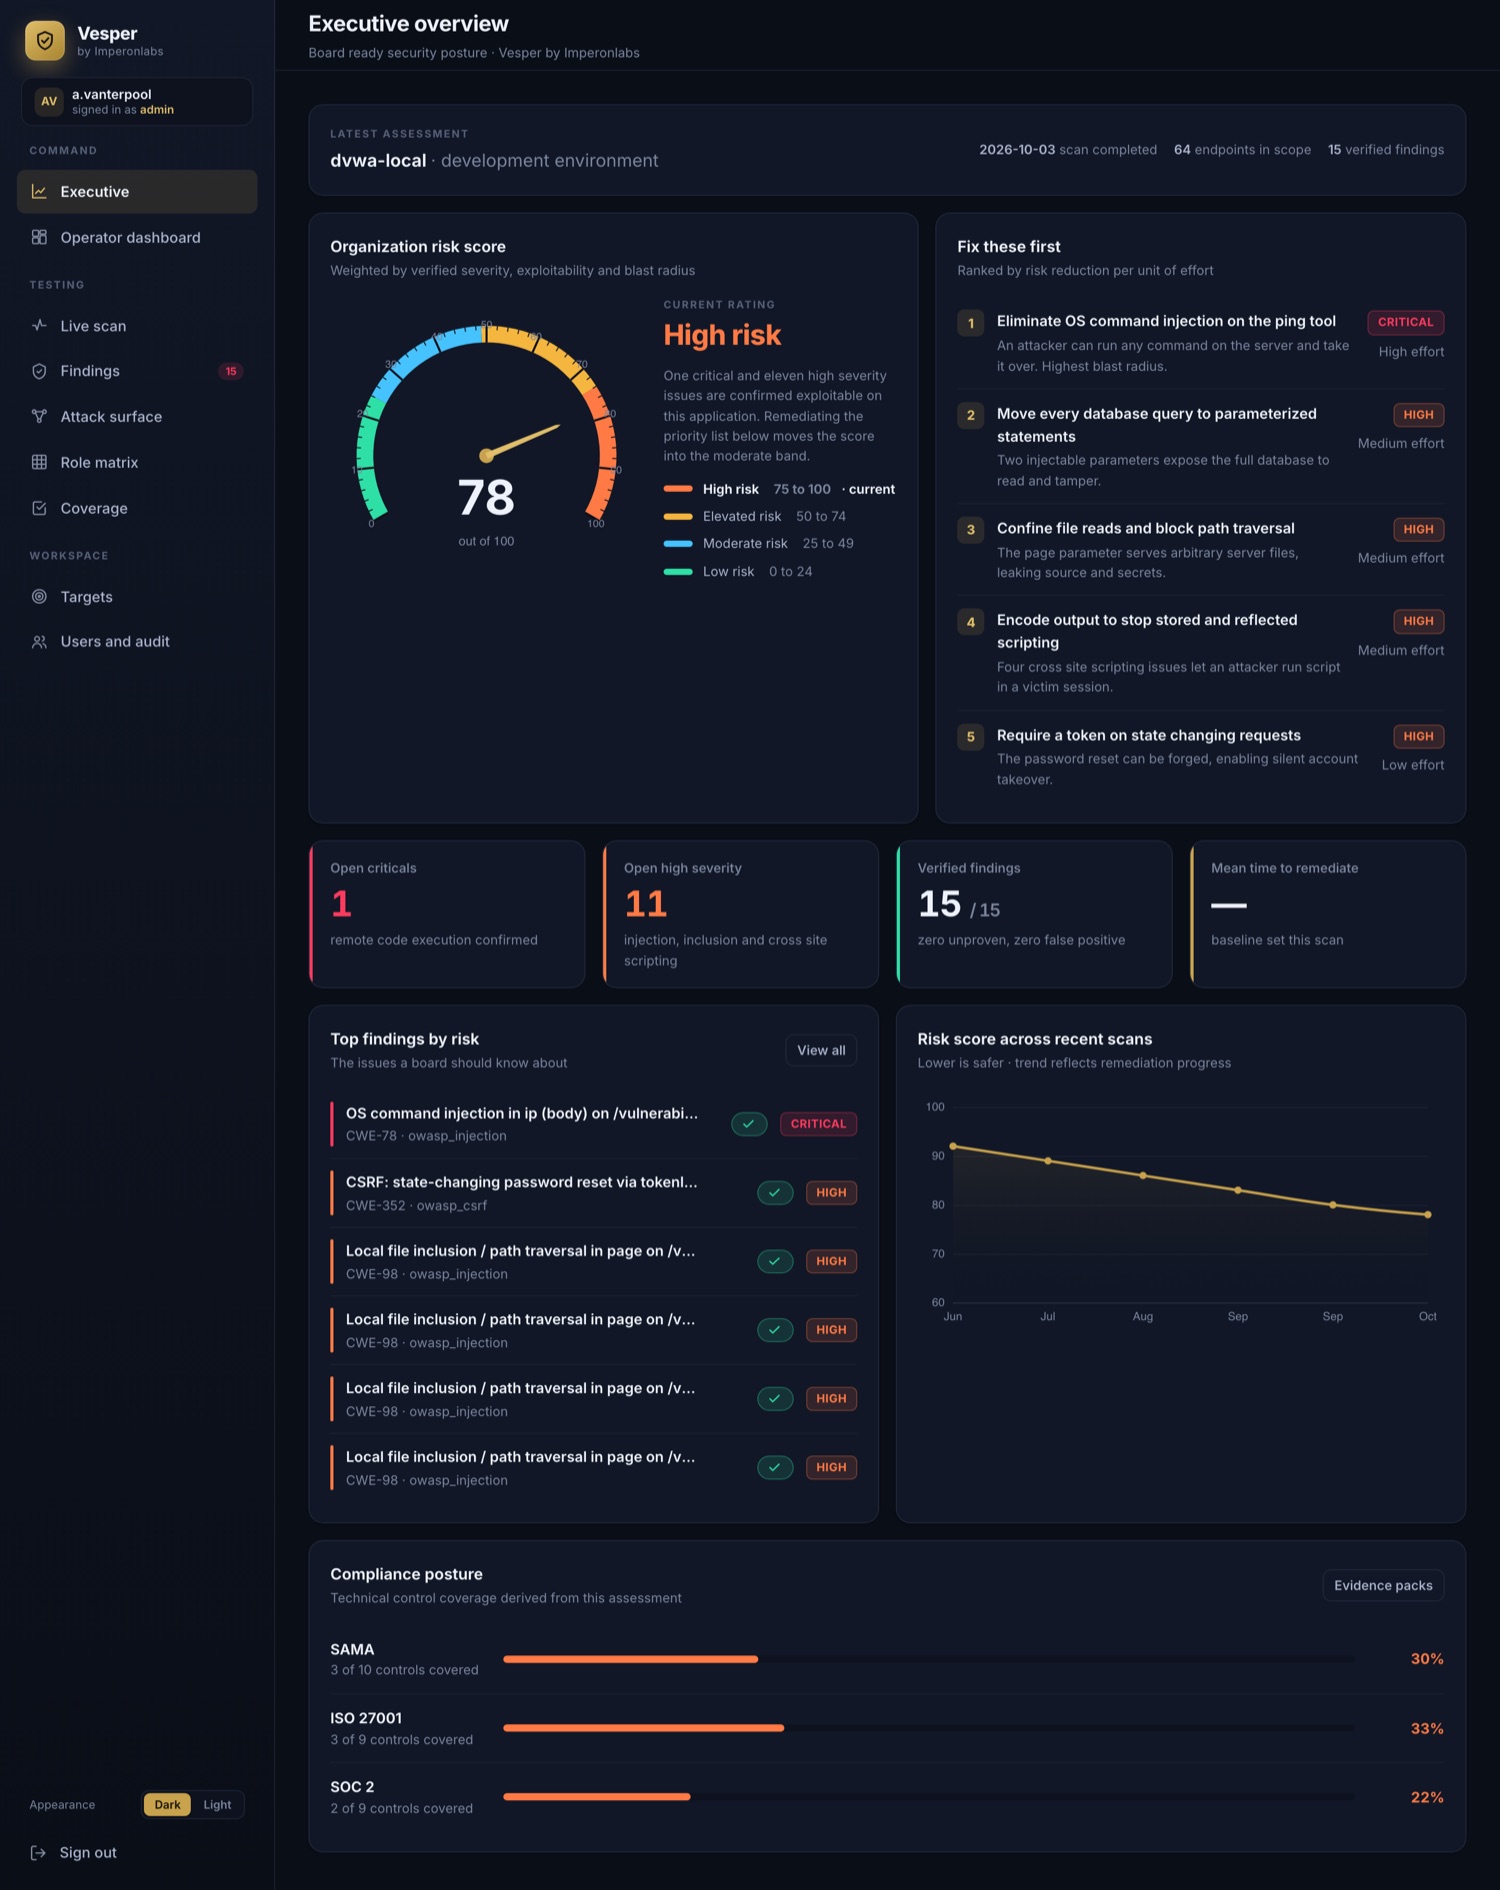
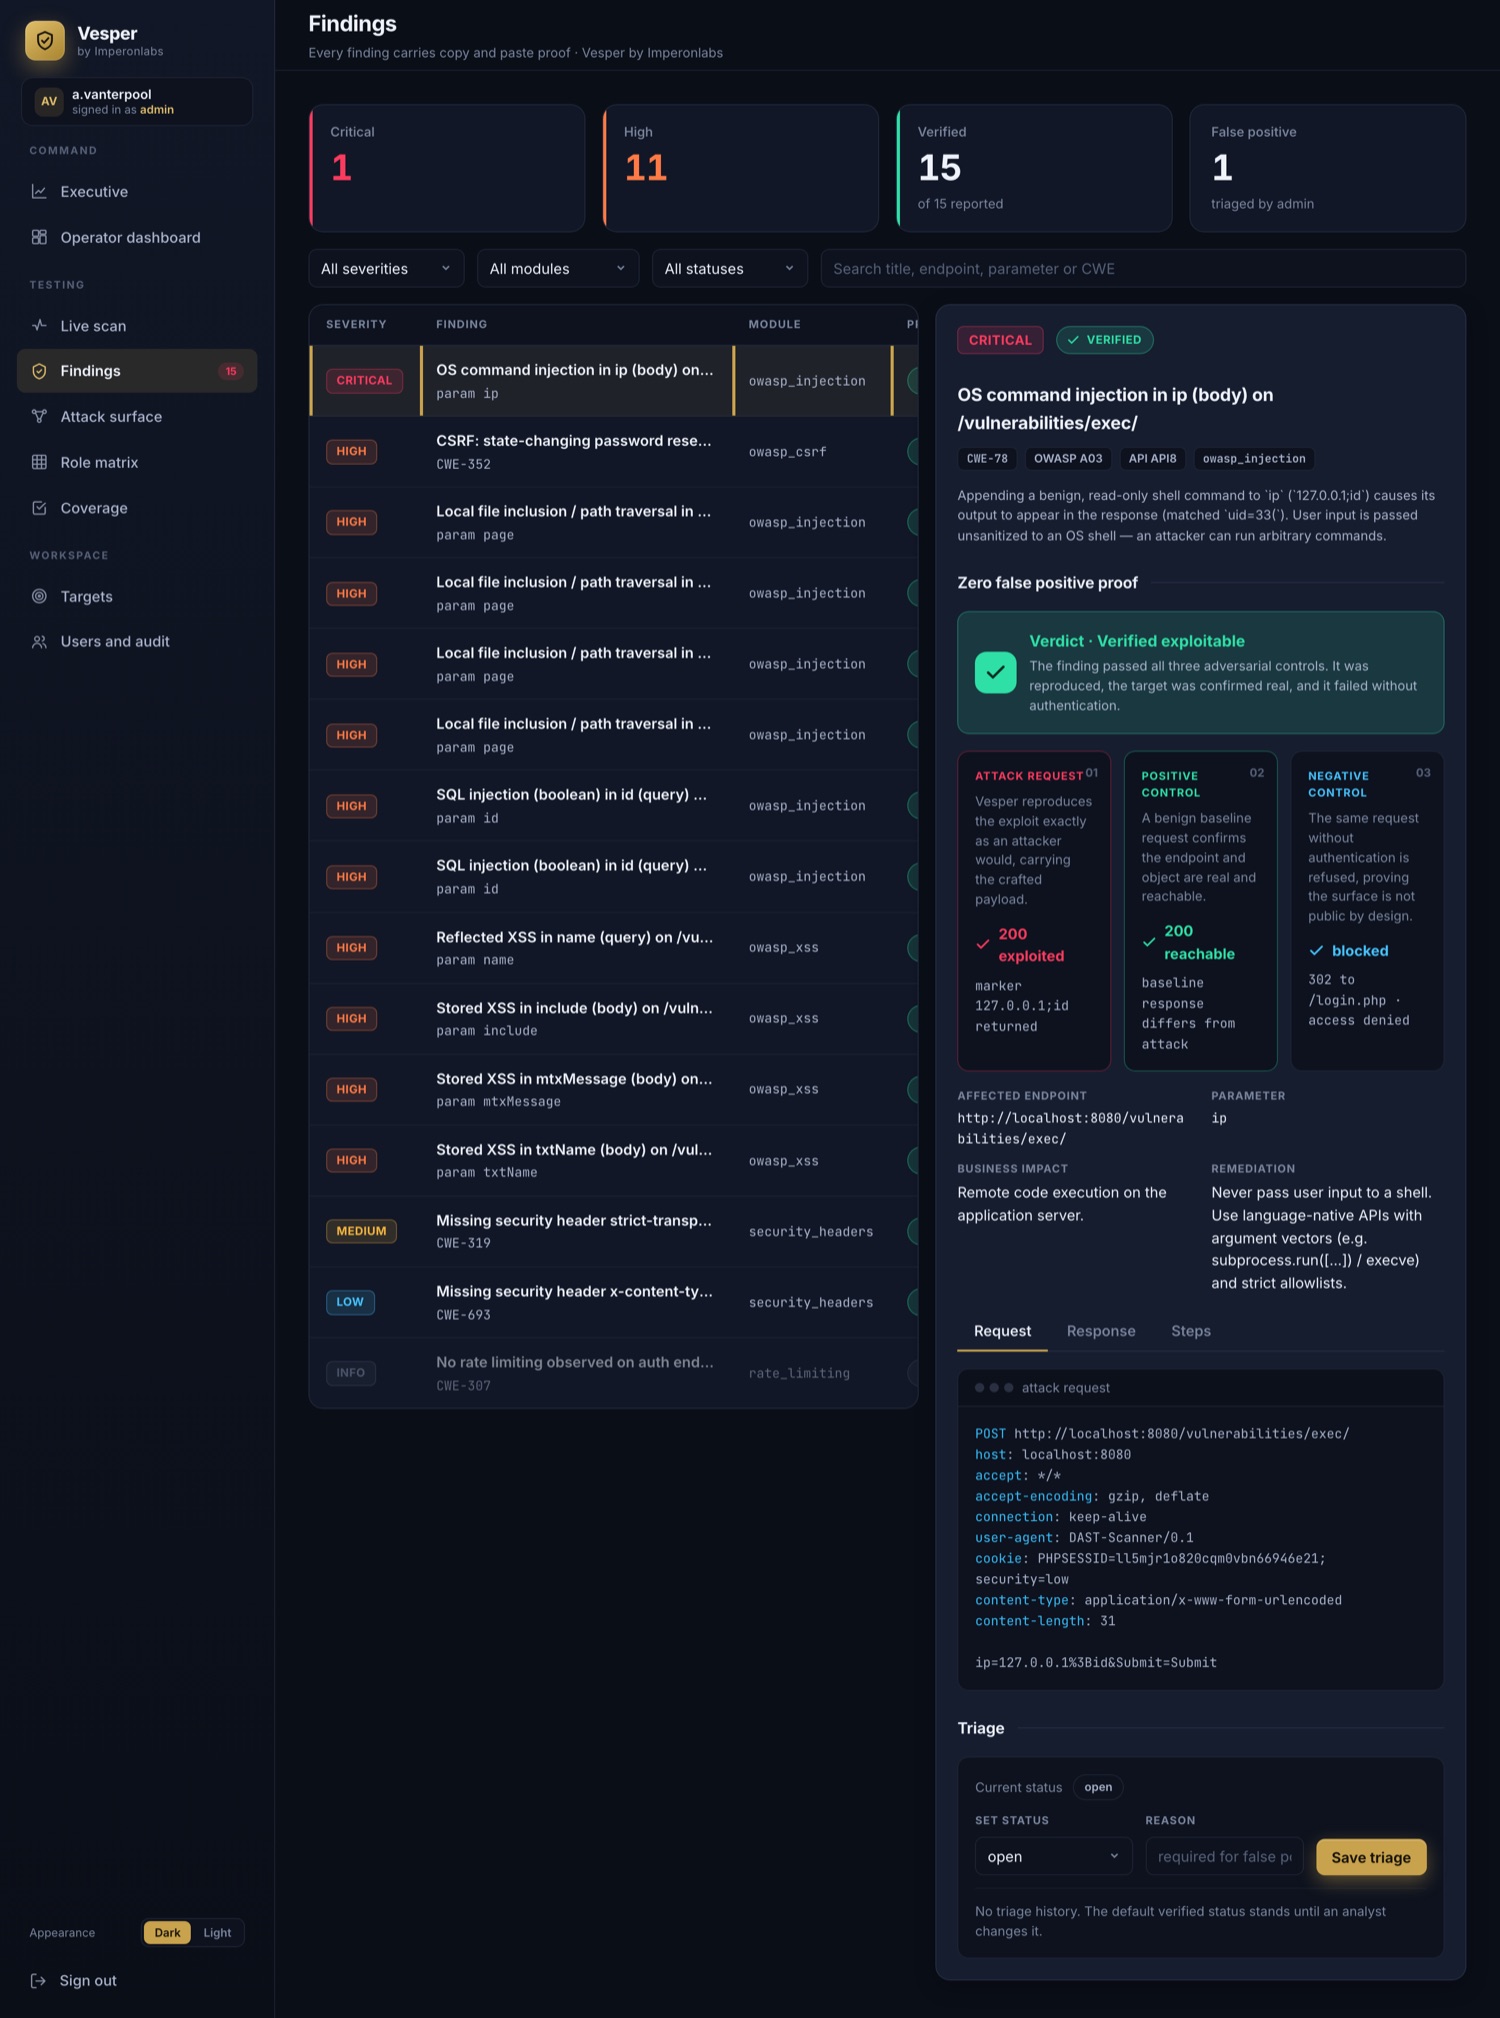
The governed console, from the boardroom view down to the proof behind a single finding. These are real screens from the product.
Vesper reproduces the attack as an attacker, confirms with a positive control that the target is genuinely reachable, and confirms with a negative control that the same request fails without authentication. Only a finding that passes all three is marked verified, each with a working proof of concept you can re-run yourself. Anything Vesper could not re-prove is reported below verified and says which leg it could not take. Detection is deterministic and reproducible, with or without AI.
Vesper verifies an authorization finding with three controls: it reproduces the attack, confirms the target is genuinely reachable, and confirms the same request fails without authentication. Findings in other classes, such as OS command injection, SSRF, CRLF injection, forged JWTs, unauthenticated reachability and stored XSS, are re-proven by re-running that class's own experiment with its own negative control, rather than by re-sending the request. Classes whose evidence is one shot, such as a race condition win, are reported below verified and say so.
One profile sets crawl depth, which modules run, payload breadth and a hard time budget that aborts gracefully and still reports what it found. Add per scan exceptions to skip rate limiting, brute force or smuggling, and Vesper records exactly what was and was not tested in a coverage report.
Shallow crawl and fast deterministic checks: headers, TLS, auth, CORS, JWT, reflected XSS, boolean SQLi and core BOLA. Built for CI gates; never wastes time on slow probes.
Browser crawl, stored XSS, the full BOLA and BFLA matrix across every role, GraphQL, time based SQLi and content discovery with tech matched wordlists. The scan to run before you ship.
Exhaustive crawl and all JS, request smuggling and desync, SSTI, DOM XSS, the full polyglot arsenal and WAF bypass variants, large wordlists and wildcard recon. For audits that have to be thorough.
Thirty seven modules across four families, thirty six of which can report a finding. Each finding carries a copy paste proof of concept.
Drop the CLI into any pipeline. Vesper returns machine readable results, gates the build on an exit code, writes SARIF for your code scanning dashboard, and emits SAMA CSF, ISO 27001 and SOC 2 control reports alongside the pentest report, ready for auditors on every run.
From startups to the largest enterprises, across web apps, APIs and every industry. If you ship software, Vesper proves what an attacker could do with it.
Prove your security to customers and investors and ship every release with confidence, without standing up a full security team.
Test your web app and API on every build, pass vendor security reviews with real evidence, and keep pace with how fast you ship.
Banks, fintech, healthcare, retail, defense and government. Authenticated testing with SAMA, ISO 27001 and SOC 2 evidence, self hosted and air gap friendly.
Deploy self hosted as a single tenant Docker image so credentials, keys and findings never leave your environment. It is health checked, non root and compose ready.
It means Vesper re-established the claim against your target during the scan, and the scan metadata records how. Every authorization finding passes a three control adversarial gate: Vesper reproduces the exploit exactly as an attacker would, confirms with a positive control that the object is genuinely reachable, and proves with a negative control that the same request fails without authentication. Differential and behavioural findings re-run their own experiment with their own negative control, 22 of the 36 finding producing modules in all. Findings that are public by design, or that cannot be reproduced, are quarantined rather than reported, and a claim Vesper could not re-prove is reported below verified and says so.
No. All detection is deterministic and runs with no AI at all. If you want it, you can plug in your own model key for optional AI triage and attack planning. Your data, your key. Strong results do not depend on AI.
Yes. Vesper supports password login, cookie or session auth, pasting a raw JWT or cookies, importing a session from HAR, and configuring an MFA / TOTP seed. Add several roles and it builds a full cross identity authorization matrix.
Both. The CLI drops into CI and agent pipelines with exit code gating and SARIF; the governed web console adds role based access control, scan history, rescan, scheduling and Slack and email alerts.
As a single tenant Docker image you self host, so credentials, keys and findings stay in your environment. It is health checked, non root and compose ready.
Vesper is the product that runs the deep authenticated assessment at machine speed and repeatability. Our offensive security services wrap human researchers around it for red team operations, bespoke business logic work and advisory. Many clients run Vesper every release and bring in the team for the high stakes, creative work.
Point Vesper at one mid size application, roughly 50 API endpoints and 8 to 10 pages, and get a verified assessment with proof on every finding, at a flat $2,000. Larger or more complex apps are scoped and quoted. See Vesper pricing, or talk to us about your portfolio.