Humans hunting, platform moving

We hunt what your
defenders never see.

Elite offensive security, continuously breaking your products before attackers do. Live findings ranked by real impact, with fixes your engineers can actually ship.

Human ledmanual first, not scanner noise
Live findingsthe moment we confirm them
Free retestsevery engagement, verified closure
Published CVEsresearchers who ship real bugs
Security work you can see

No blind box. Watch the work move.

Coverage, evidence, remediation and retests in one continuous workflow, powered by Raptor recon and our finding engine. You see findings the moment we confirm them, not in a PDF three weeks later.

RAPTOR Β· recon at machine scale discoverenumerateexploitverify 47 assets mapped LIVE FINDINGS CRIT Cross tenant object access on /exportsapi.acme.ioconfirmed HIGH SSRF to cloud metadata, temp credentials readapp.acme.ioconfirmed MED Business logic: coupon applied twiceshop.acme.ioretesting FIX BFLA on employee directoryhr.acme.ioverified closed
Flagship product

Meet Vesper. Proof, not noise.

Vesper is our offensive security platform. It logs in like a real attacker, maps your whole web app and API, and tries to refute its own findings before it reports them. You get evidence you can re-run, not noise, from a CLI or a governed console, with or without AI. Built for teams of every size and industry, from a first startup product to a global enterprise estate.

  • Authorization findings proven by cross identity attack, with a positive and a negative control
  • Full BOLA, BFLA and privilege escalation matrix across every role
  • 37 web and API attack modules, each finding with a copy paste proof
  • Compliance packs on every scan: SAMA, ISO 27001, SOC 2
  • Runs in your CI with SARIF, strong with or without AI
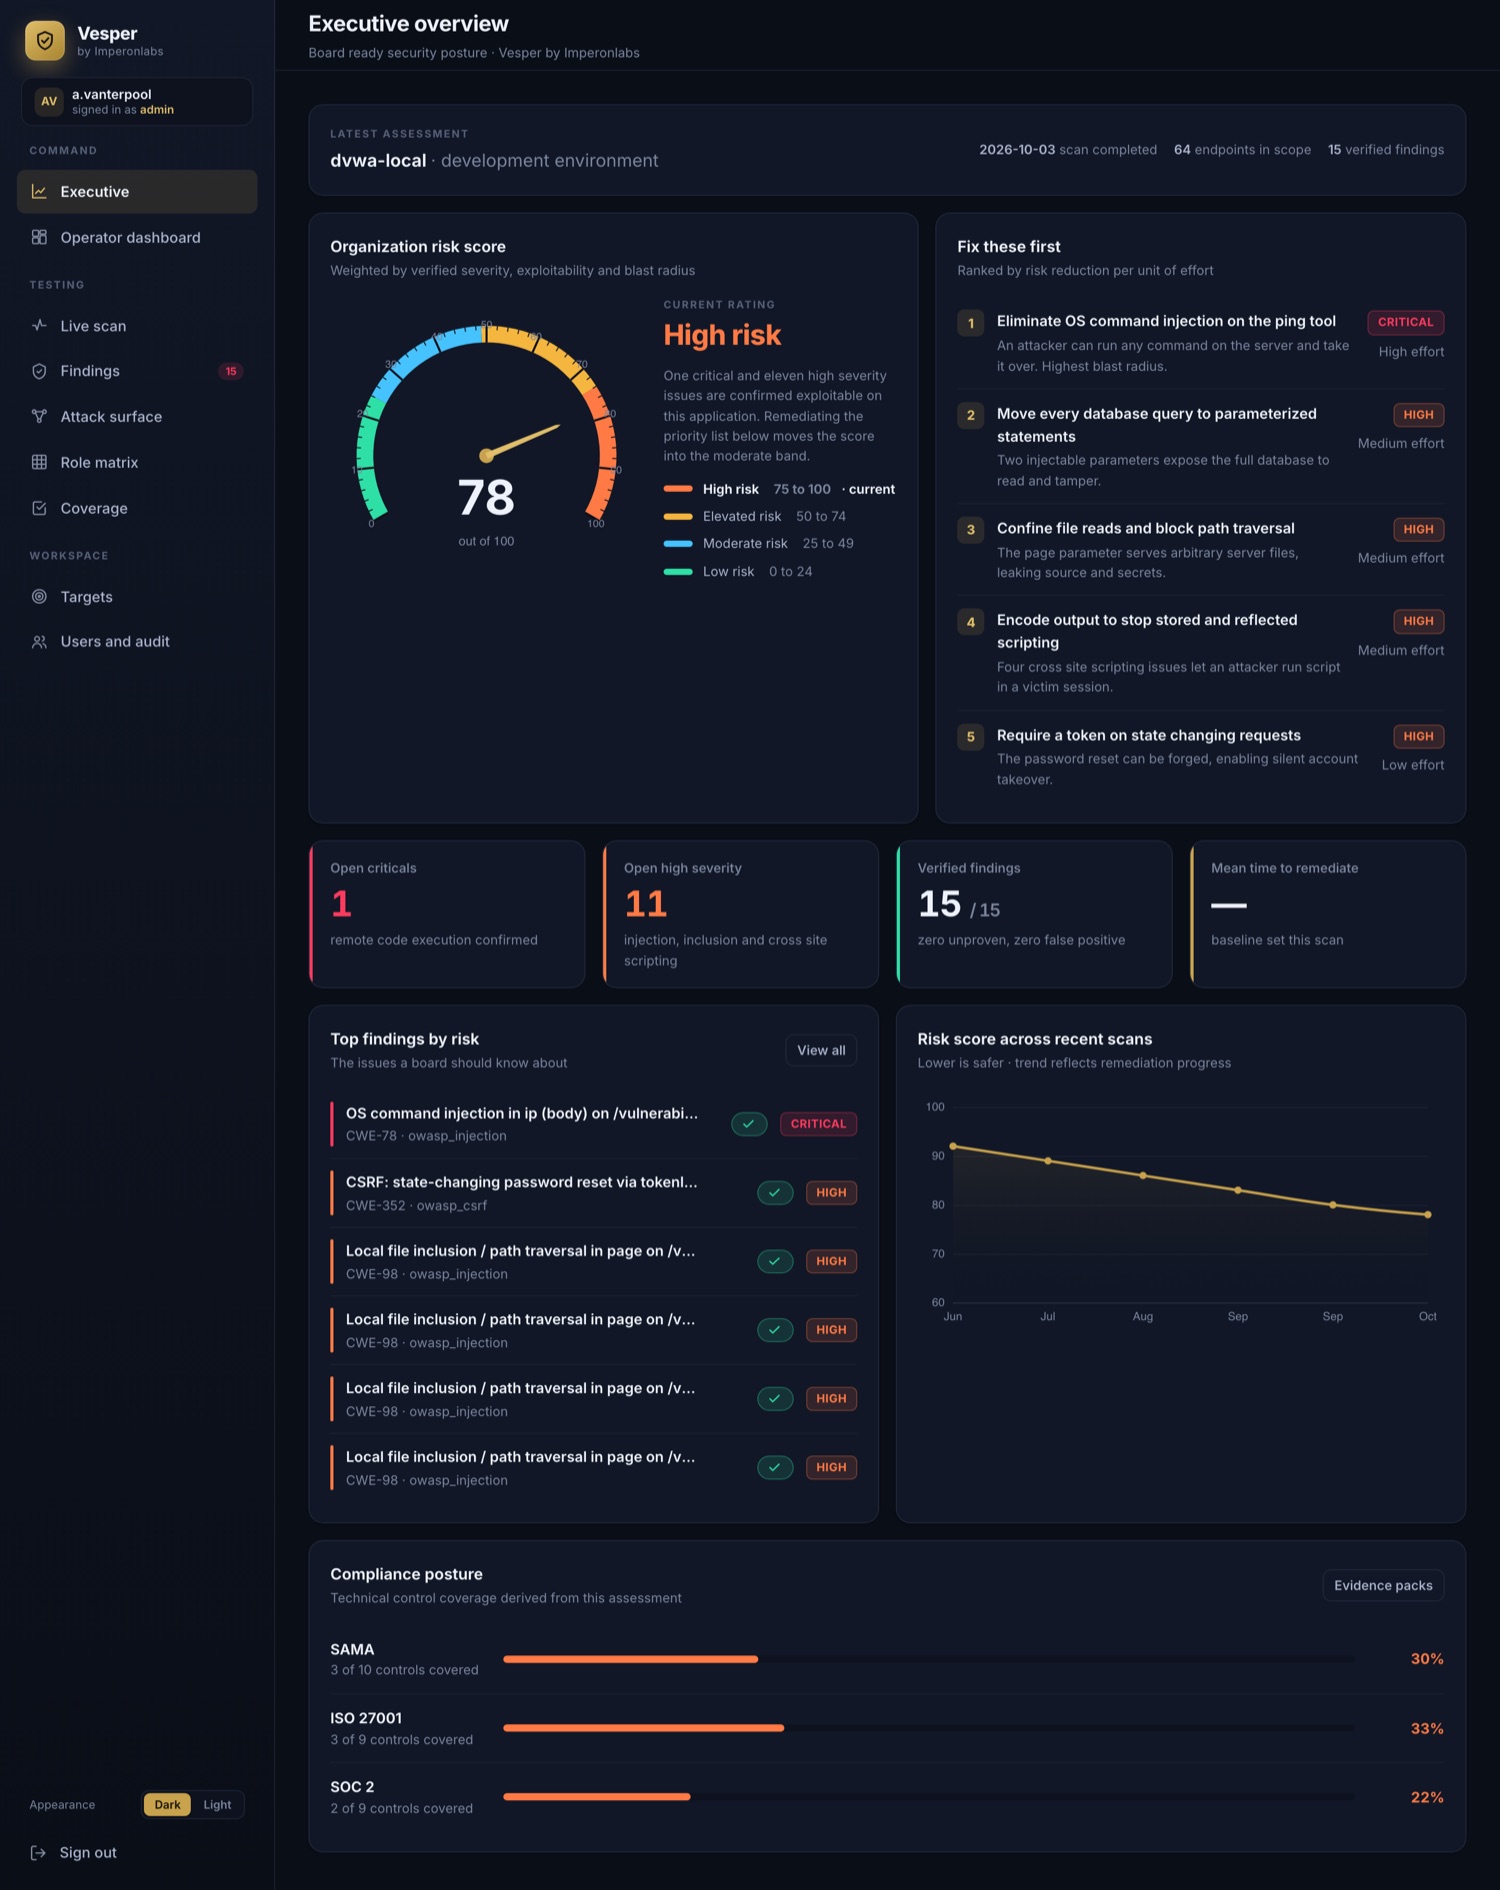
Vesper executive overview dashboard: organization risk score, prioritized fixes and SAMA, ISO 27001 and SOC 2 compliance posture.
Adversarial re-proof, live

Vesper verifies an authorization finding with three controls: it reproduces the attack, confirms the target is genuinely reachable, and confirms the same request fails without authentication. Findings in other classes are re-proven by re-running that class's own experiment with its own negative control, rather than by re-sending the request. Classes whose evidence is one shot are reported below verified and say so.

One team, every surface

Point us at the thing keeping you up.

Manual, exploit driven testing across your whole product surface, sold as a pool of testing hours you spend where the risk is, not one off per app quotes.

πŸ•ΈοΈ

Web application testing

Auth, authorization, tenant isolation, business logic and data paths. The flaws attackers use to compromise SaaS.

business logictenant isolationOWASP
πŸ”Œ

API security testing

REST and GraphQL. BOLA, BFLA, mass assignment, excessive data exposure, JWT gaps and abuse paths scanners miss.

BOLAGraphQLmass assignment
πŸ€–

AI and LLM testing

Prompt injection, tool abuse, agentic workflow manipulation and guardrail bypass. Secure AI before conversations become actions.

prompt injectionagenticguardrail bypass
☁️

Cloud security assessment

AWS, Azure, GCP. IAM abuse paths, public exposure, storage misconfig, secrets and the logging gaps that hide the rest.

IAMexposuresecrets
πŸ“±

Mobile security

Client controls, local storage, transport, reverse engineering resistance and the backend API trust boundary.

runtimelocal storage
🎯

Red team operations

Objective based exercises that measure prevention, detection and response, not a checklist of open ports.

detection gapsobjective based
πŸ”

Secure code review

The high risk paths scanners miss: auth, payment, crypto and data handling, read by people who exploit for a living.

authpayment flows
πŸ›°οΈ

External attack surface

Know what attackers can see first. Exposed assets, forgotten services, risky DNS and login surfaces, continuously.

exposed servicesshadow IT
🧭

Security consulting

Roadmap, architecture review, remediation planning and executive risk clarity, before the pressure hits.

architectureadvisory
The difference

Most pentests waste your time. This one will not.

The usual pentest

  • A black box PDF that lands weeks after the test ends
  • Junior testers running someone else's checklist
  • Scanner output reformatted as findings
  • A retest that costs extra and takes weeks

Working with us

  • Live findings the moment we confirm them
  • Researchers who ship CVEs and hunt for a living
  • Manual exploitation with proof, ranked by real impact
  • Free retests, closure the next scan proves
Research and field notes

The work speaks. So does the writing.

We publish the real methodology behind the findings. Read the field notes.

How an engagement works

From scope to proven closure.

Four steps, no black box. You see the work move the whole way through.

01

Scope & authorize

We agree the assets, the depth and the rules of engagement, and send a fixed quote before any testing starts.

02

Hunt

Manual, exploit driven testing across your surface. Real attacks, safe execution, evidence for everything.

03

Live findings

You get each finding the moment we confirm it, ranked by real business impact, with a fix your team can ship.

04

Retest to closure

We break every fix again. A finding is closed only when the fix holds, not when a ticket is marked done.

Questions

Frequently asked.

What does Imperon Labs do?

Imperon Labs is an offensive security company. We run continuous penetration testing, red team operations and attack surface management, and we build security products for attack surface management, vulnerability assessment and threat intelligence. In short: we break your products before real attackers do.

How is this different from a scanner or automated pentest?

Scanners find known patterns. We find the exploitable risk they miss: broken access control, authentication and tenant isolation failures, business logic abuse, and the chains that turn a small bug into a breach. Every finding is manually exploited, proven with evidence, and ranked by real impact.

Do you retest fixes?

Yes, and it is included. We break every remediation again and only mark a finding closed once the fix holds. You get proven closure, not a green tick.

What can you test?

Web and mobile apps, APIs, cloud environments, internal and external networks, AI systems, and source code. We also run compliance driven testing for ISO 27001, SOC 2 and PCI DSS.

How fast can you start?

Most engagements are scoped and underway within days. Because findings are delivered live, you start seeing value during the test, not in a PDF three weeks later.

Who founded Imperon Labs?

Imperon Labs was founded by Yash Pandya, who serves as Founder and CEO. A security researcher by passion with more than 15 years of experience, he also serves as Head of Product Security at a fintech. He has been recognized and rewarded by many companies through their bug bounty programs and has published multiple security advisories and CVEs in widely used open source software such as Apache, ImageMagick, Jackson FasterXML and LibRaw, with vulnerabilities also acknowledged by Apple, Microsoft, Google and Uber, among more than 100 organizations. Read more on the about page.

Find out before they do

Start a hunt this week.

Tell us the asset, the deadline, and the decision you need to support. We map the right engagement and respond within a few hours.

Review my scope